Cloudflare · setup · 2026
Cloudflare SSL/TLS
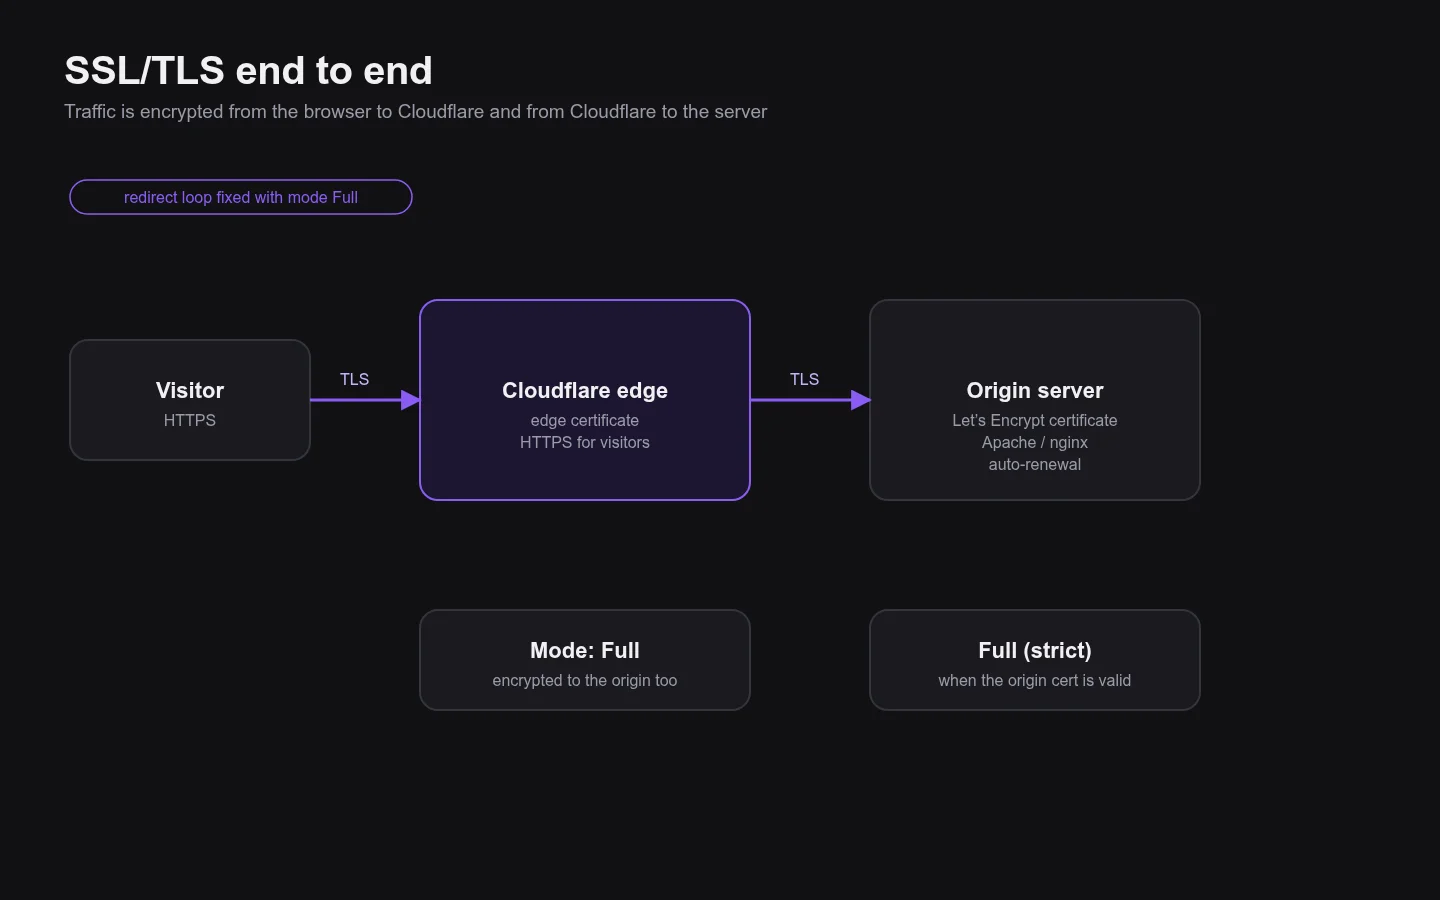
HTTPS from the browser to the server: Cloudflare edge certificates, Let’s Encrypt on the origin and real visitor IPs behind the proxy.
About the project
Sites use SSL mode Full, so traffic is encrypted to the origin too — this also fixed a redirect loop on one of the servers. Origin certificates are issued and renewed by Let’s Encrypt.
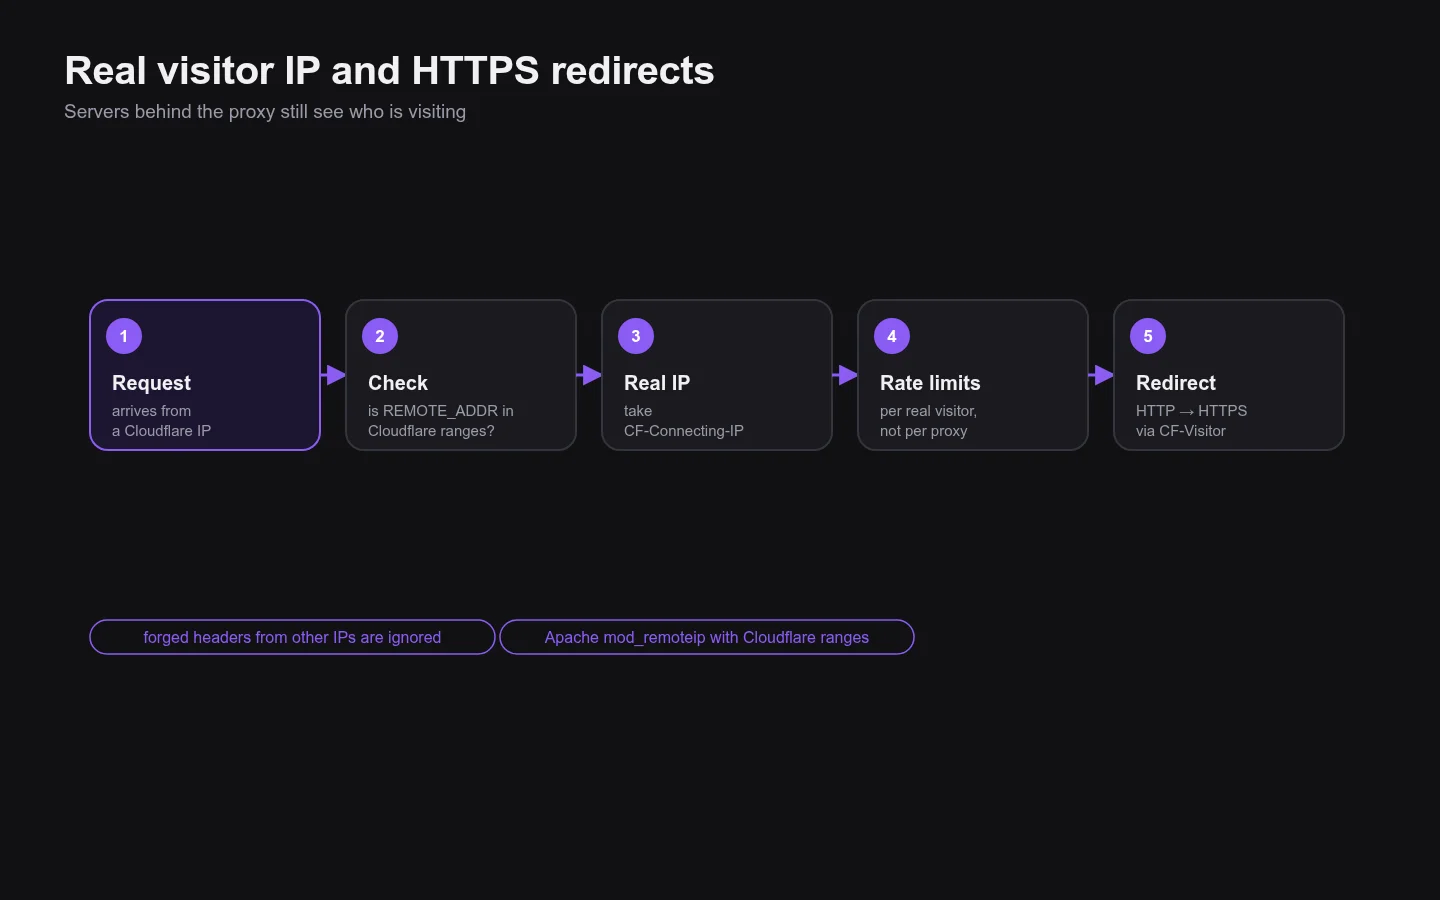
Behind the proxy every request comes from a Cloudflare address. Servers take the visitor IP from CF-Connecting-IP only when the request really comes from Cloudflare ranges, so rate limits work per visitor.
What I did
- SSL mode Full, encrypted to the origin
- Let’s Encrypt certificates with auto-renewal
- HTTP → HTTPS redirects that work behind the proxy
- Real visitor IP via Apache mod_remoteip
- Forged IP headers ignored
Year
2026
Type
Cloudflare · setup
Stack
Cloudflare SSL/TLS, Let’s Encrypt, Apache
Screens